
Solution · Subsidiaries
Evaluating Subsidiaries
Enterprises can own hundreds of subsidiaries across locations and time zones. If a subsidiary is breached, the parent company is affected and liable too, so it’s important to assess and monitor the cyber risk of every subsidiary.
Assess
Assess Your Subsidiaries’ Cyber Risk
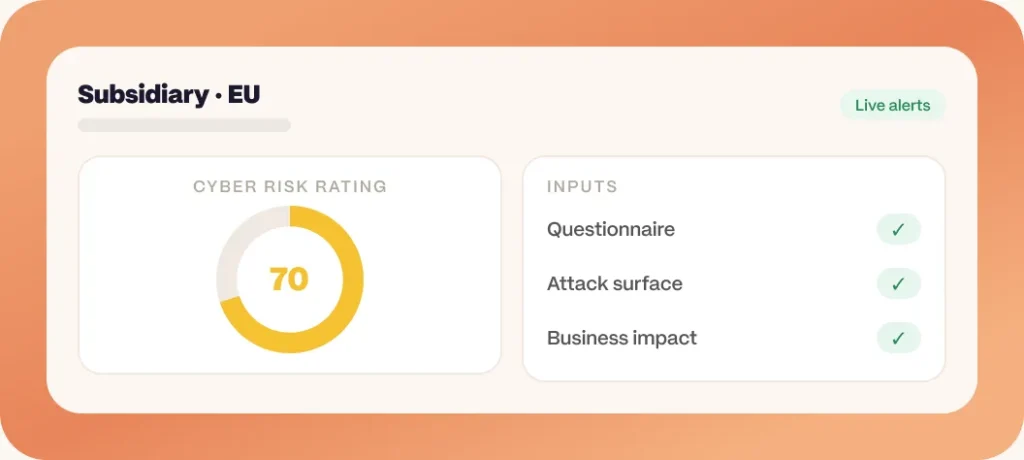
Panorays’ Cyber Risk Rating combines security questionnaire responses, attack surface assessment and business impact. Continuous monitoring sends live alerts on changes, with remediation plans for every gap.
Compliance
Comply with Regulations
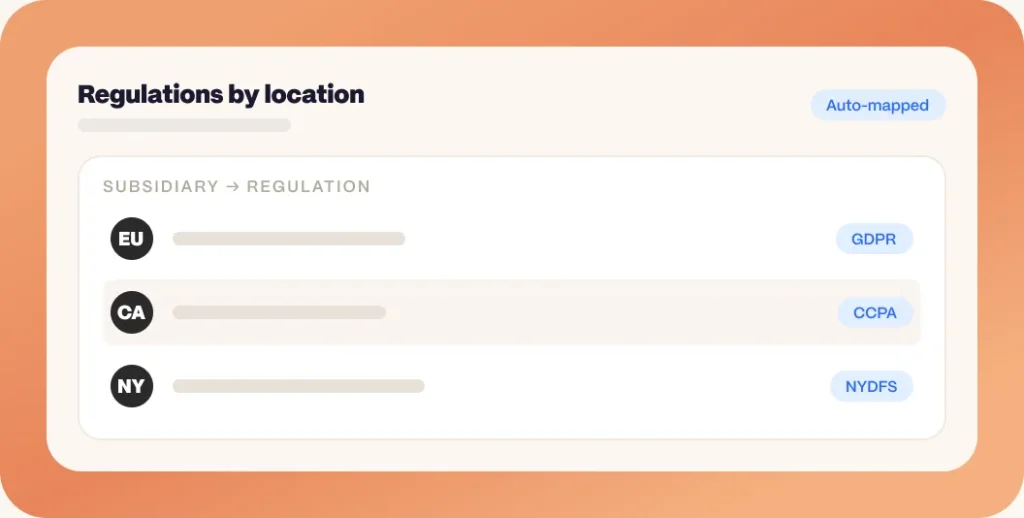
Smart Questionnaires determine which regulations each subsidiary must meet based on its location (GDPR, CCPA, NYDFS), and the platform keeps documentation for regulations like OCC and EBA.
Collaboration
Engage with Your Subsidiaries
Parent companies and subsidiaries work on the same platform to dispute findings, validate results and report mitigation progress. Direct messaging removes false positives and communication gaps.
Assess your subsidiaries’ compliance

PCI
AICPA SOC
ISO
GDPR
CCPA
Related Resources
 Guides
12 Essential Questions to Determine Third-Party GDPR Readiness
Best practices for helping your third parties comply with GDPR.
 Webinars & Videos
Context: The Missing Piece in Your Third-Party Security Program
Your third-party security program involves 3 stakeholders: the business owner, you as the representative of the security and risk team and the…
AppsFlyer Case Study
AppsFlyer accelerates and streamlines vendor security risk management, enabling seamless processes and scalability.