
Regulatory Compliance Monitoring
Easily ensure supplier compliance with regulations
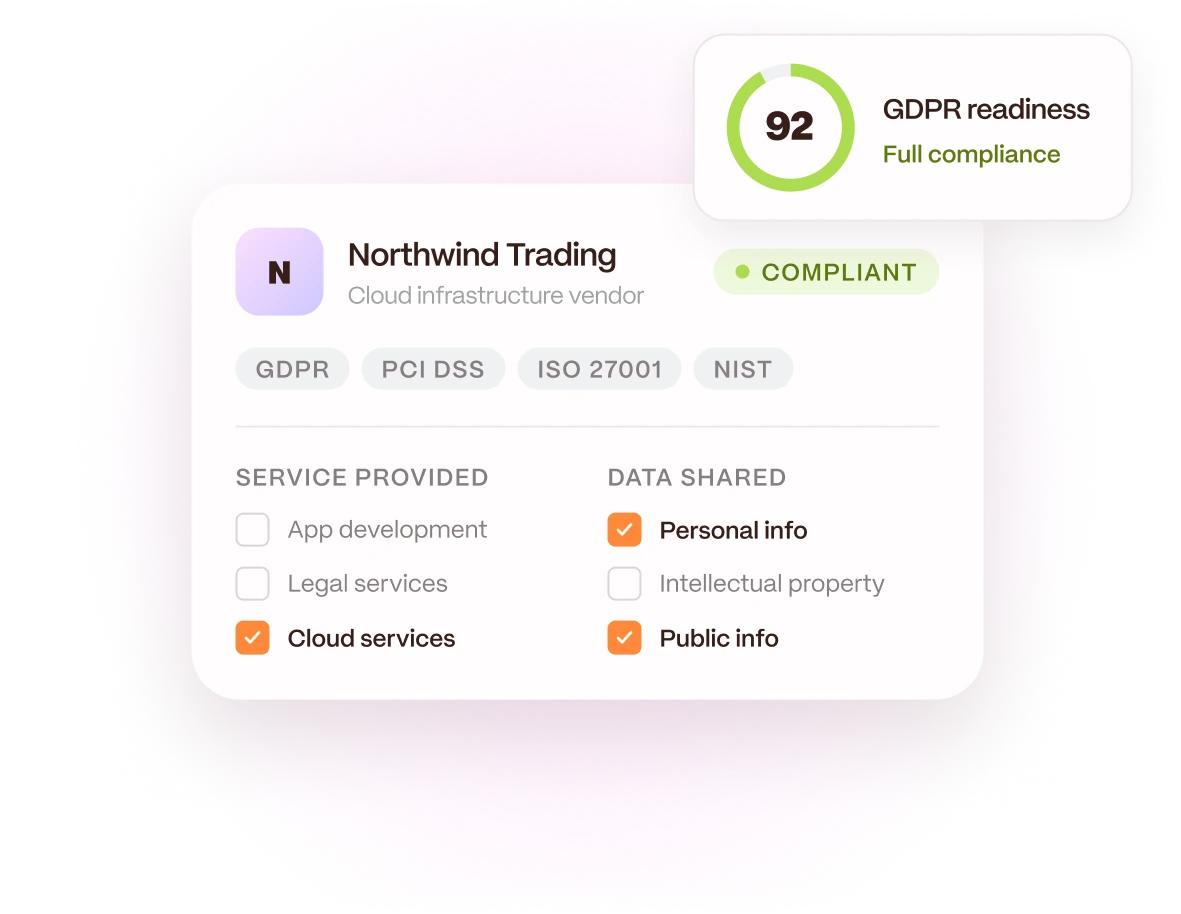
You determine who needs to comply, and Panorays checks that they do.
Trusted by Hundreds of Teams for Third-Party Cyber Risk Management
How it works
Everything you need to keep every supplier compliant
Define who has to comply, and Panorays handles the checks, evidence and monitoring no spreadsheets required.
Panorays provides one location where all relevant teams can connect and find the information they need – without calling or meeting with each other.
 Sam Potashnick, Information Systems Team Leader, Payoneer
Explore more Panorays capabilities
Reporting & dashboard
Present your supplier portfolio to stakeholders and teams in one clear view.
Portfolio management
Seamlessly manage your suppliers’ security posture from a single portfolio.
Continuous cyber monitoring
Stay ahead of rising threats and monitor changes in third-party cyber posture.
So do we click?
See how Panorays takes control of third-party cyber risk from onboarding to remediation.