Trusted by 500+ global enterprises

Access Free Vendor Cybersecurity Reports

Instantly download security reports and cybersecurity analyses.

What’s inside a Panorays cybersecurity report?

Each Panorays security report provides an in-depth snapshot of a company’s external cyber posture. Our reports are generated using continuous, automated assessments that combine external attack surface data and proprietary Panorays analytics, offering a comprehensive view of your vendor’s security readiness.

Our Vendor Cybersecurity Reports include:

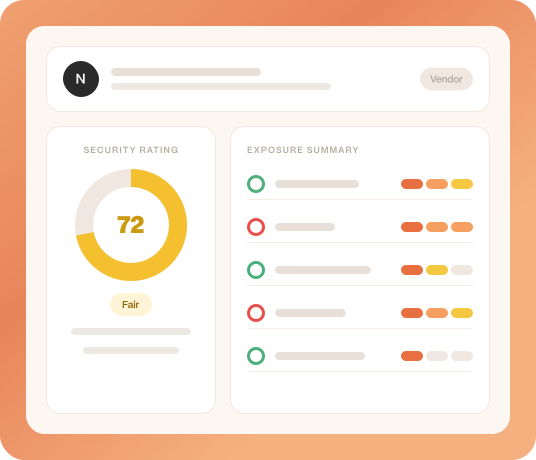
  • Vendor security rating and exposure summary
  • Attack surface mapping (IP, cloud, domain footprint)
  • Historical breach data and open vulnerabilities
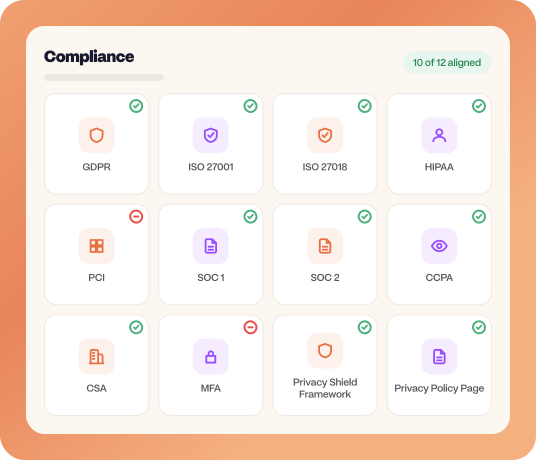
  • Compliance insights (GDPR, NIST, DORA alignment)
  • Risk prioritization and remediation recommendations
  • Comparison to industry benchmarks

For CISOs, vendor risk managers, CROs, and third-party risk teams

Make informed security decisions faster.

Panorays’ free cybersecurity reports give your team instant visibility into a vendor’s external risk posture, helping you identify vulnerabilities, validate security claims, and streamline your third-party risk management process.

Use Panorays cybersecurity reports to:

Find risk data on any public company in minutes

Quickly assess vendors before onboarding or renewals.

Share security insights with executives and boards

Generate professional, easy-to-understand reports to support risk discussions and compliance reviews.

Prepare for audits and frameworks like SOC 2 or ISO 27001

Leverage verified data and benchmarks to strengthen audit readiness.

Kick off vendor assessments confidently

Use as a starting point for deeper risk reviews or due diligence processes.

Over 3,000 free reports accessed by top firms.

Get your company’s
live security report

Security Reports: Frequently Asked Questions (FAQ)

What is a vendor security report?

A vendor security report is a detailed evaluation of a company’s external cybersecurity posture. It highlights exposure points, vulnerabilities, and compliance gaps, helping you understand how secure your third-party vendors are before you engage or renew contracts.

What’s the best way to evaluate vendor security?

The most effective approach combines automated external assessments with direct vendor input. Panorays enables you to instantly access public security data and request internal security questionnaires from vendors, giving you a complete and continuous view of risk.

How accurate are the ratings in Panorays reports?

Panorays ratings are continuously updated using real-time data from external attack surface scans, open-source intelligence (OSINT), and proprietary analytics. This ensures accuracy and reflects each vendor’s true security posture at any given time.

Can I request a full risk assessment after downloading a free report?

Yes. You can request a full, collaborative assessment through the Panorays platform. This includes direct engagement with the vendor, detailed risk validation, and remediation recommendations tailored to your organization’s security requirements.

How often are these reports updated?

Reports are refreshed regularly as new data becomes available, ensuring that changes in a vendor’s infrastructure, security posture, or known vulnerabilities are reflected in near real time.

Do I need to sign up to access the reports?

You can instantly access and download many reports for free without registration. For more advanced analytics, vendor engagement, or continuous monitoring, creating a Panorays account unlocks the full suite of capabilities.

Are the reports compliant with GDPR or DORA?

Yes. Panorays follows strict data privacy and regulatory standards. Our assessments include insights aligned with major compliance frameworks such as GDPR, NIST, and DORA, helping you evaluate third-party vendors in line with industry and regional requirements.