
Platform · Remediation
Remediation Plans for Third-Party Vulnerabilities
Improve your suppliers’ security according to your risk appetite. You set the security goal for your suppliers and they receive instructions on how to achieve it.
Trusted by Hundreds of Teams for Third-Party Cyber Risk Management
Send Your Third-Party Vendor One Aggregated Remediation Plan
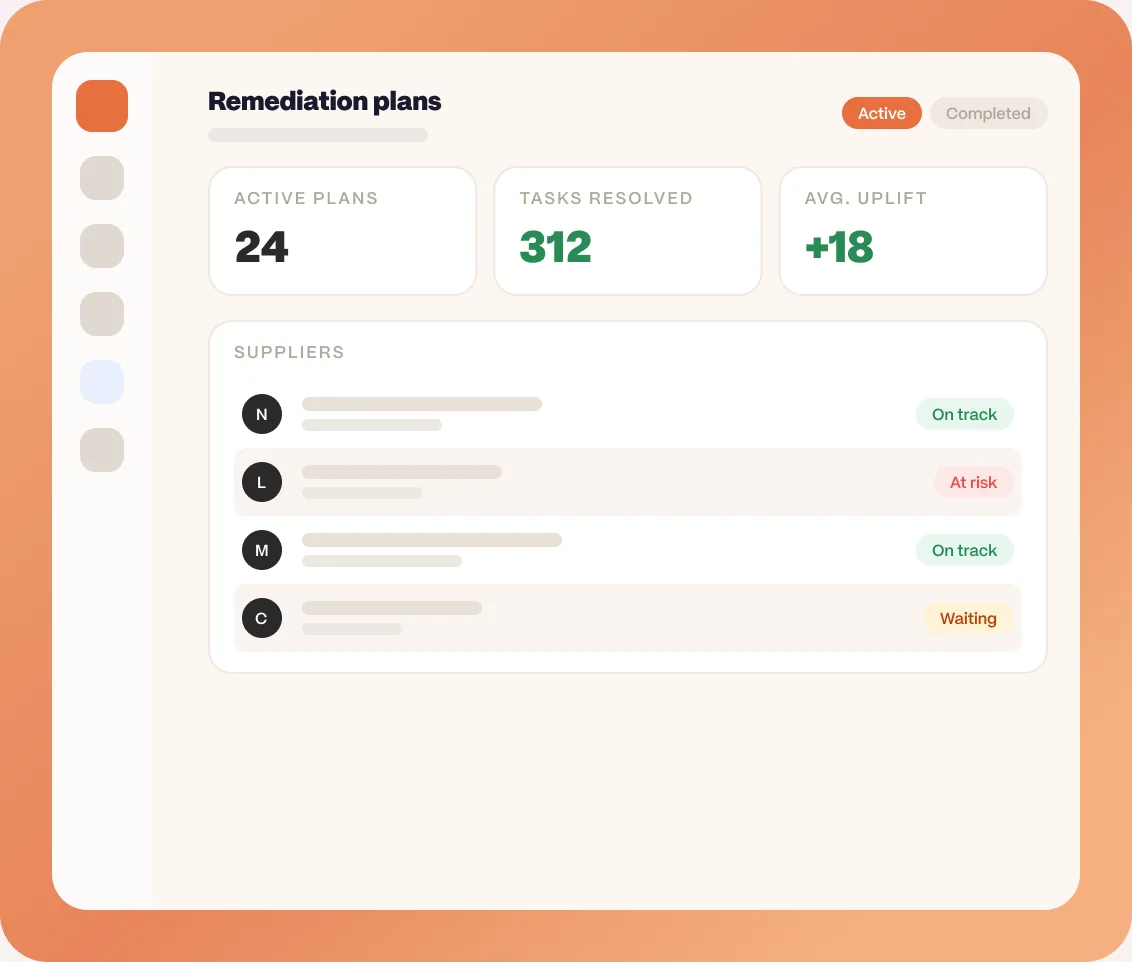
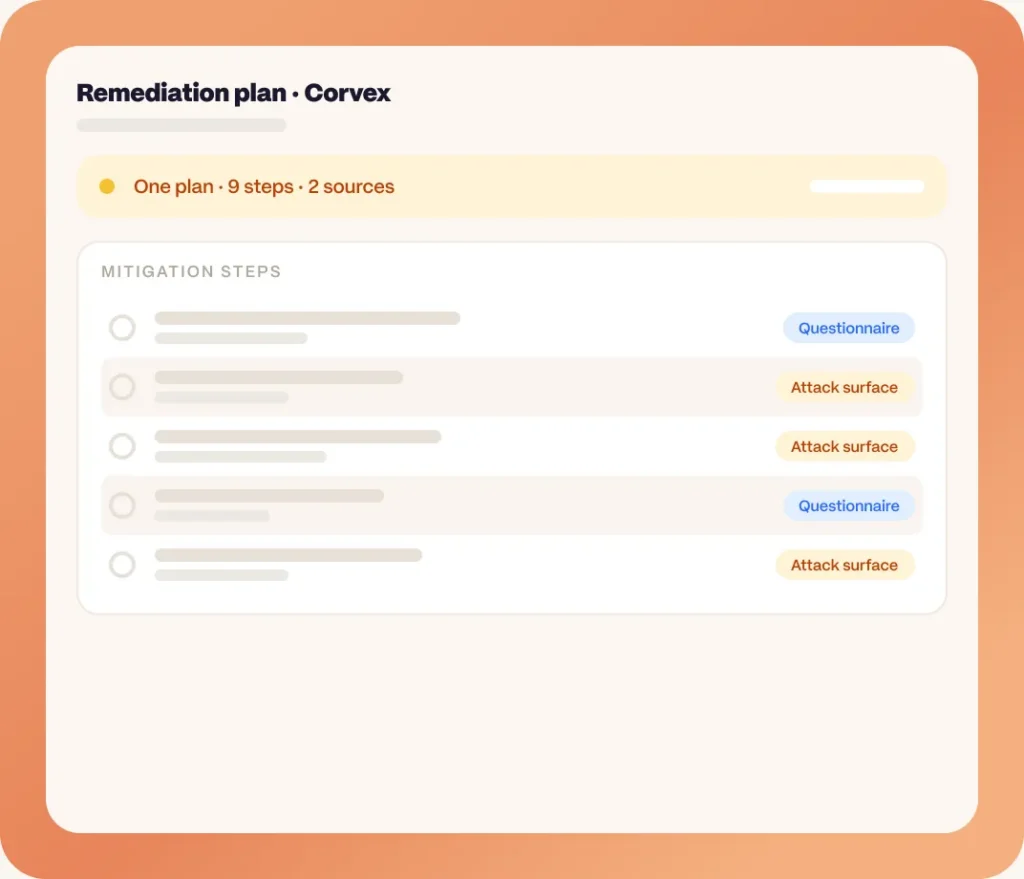
Panorays generates a prioritized remediation plan for each vendor with mitigation steps for gaps in both the Smart Questionnaire™ and external attack surface assessment.
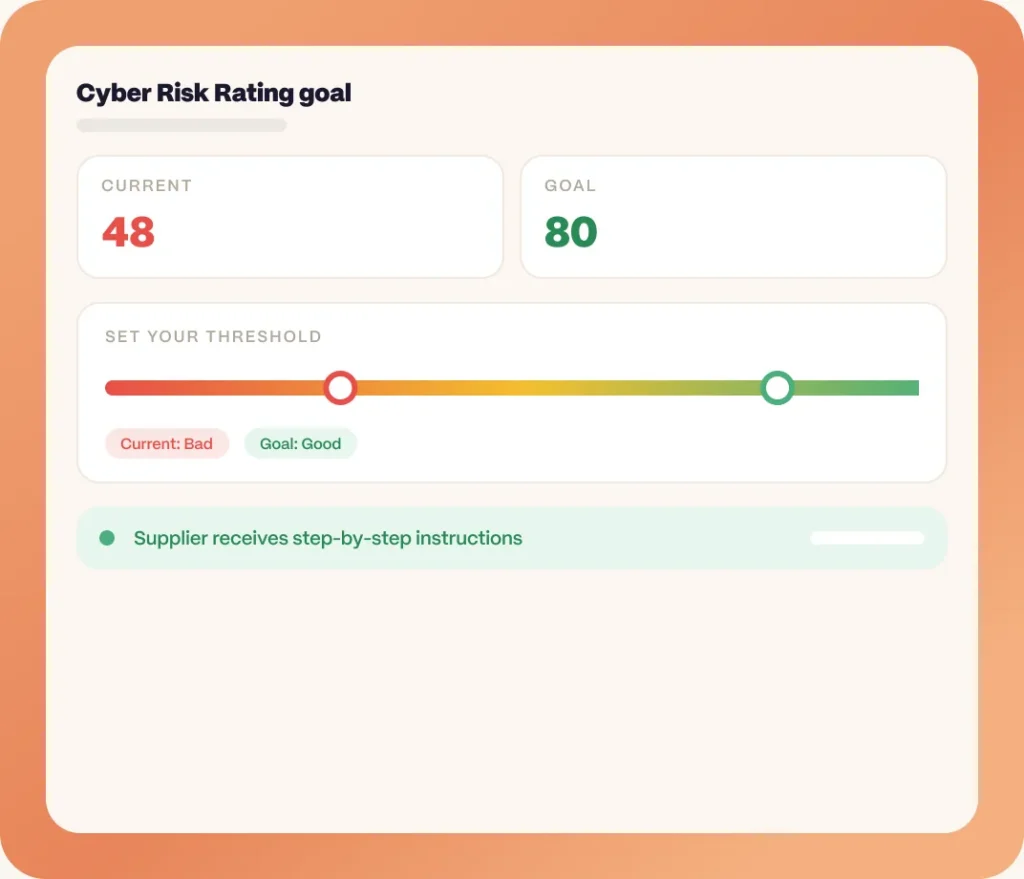
Choose Your Cybersecurity Threshold
Your supplier’s Cyber Risk Rating provides the starting point, and you determine the end point. For example, if the Cyber Risk Rating is “bad,” you can set a goal to raise it to “good.”
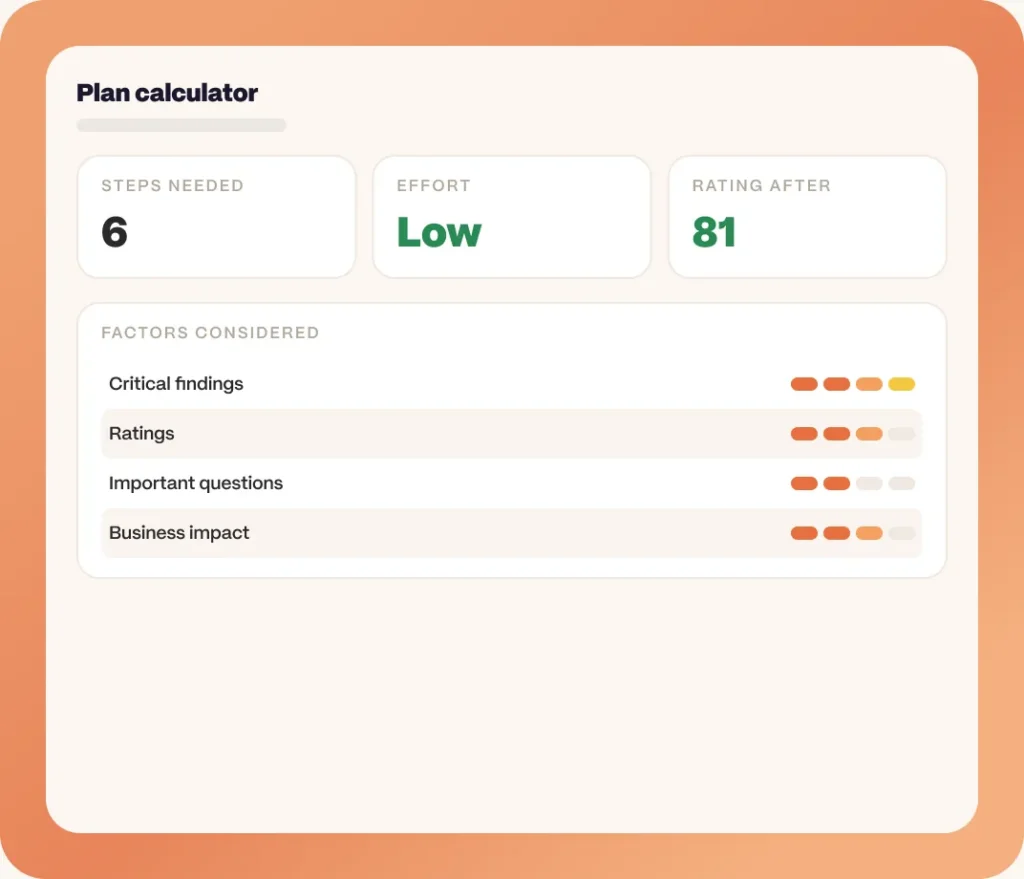
Generate a Customized Remediation Plan
Each remediation plan considers your goals and factors like critical findings, ratings, important questions and business impact. The algorithm then calculates the least number of steps and effort to reach the desired level.
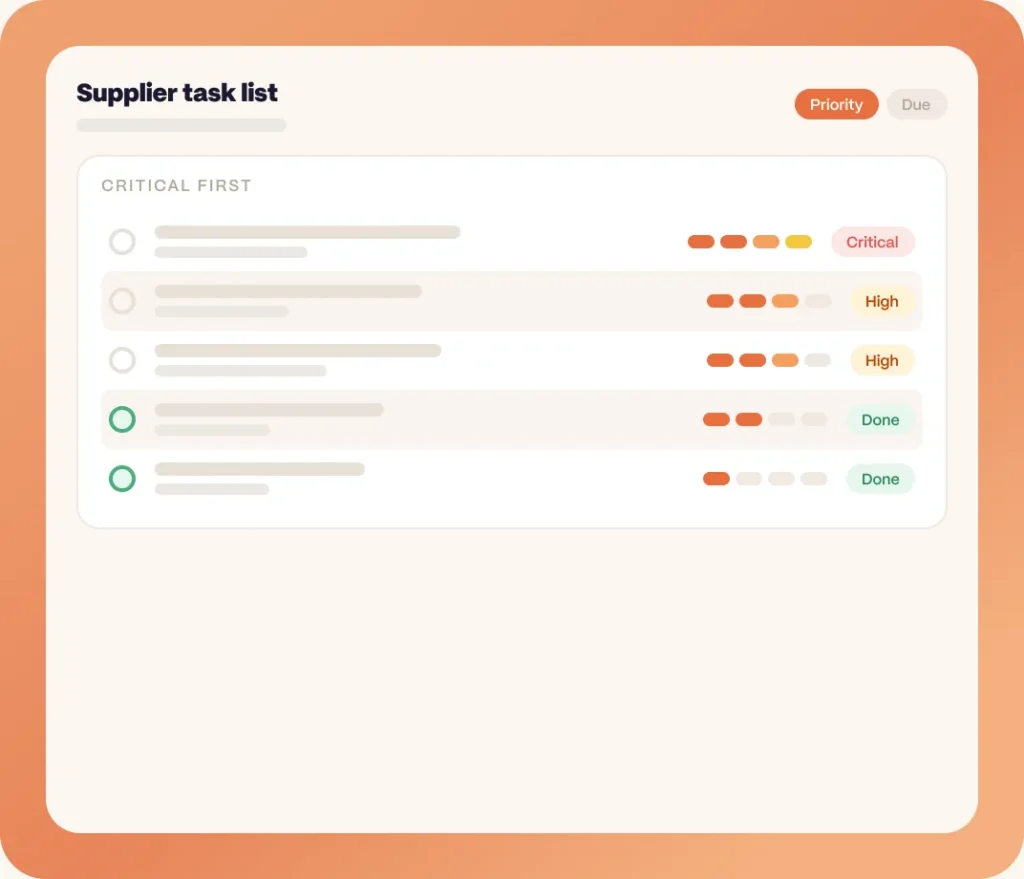
Prioritize Remediation Tasks
Your suppliers receive a list of critical tasks that should be performed to improve cyber posture. That way, they can focus efforts on addressing the most important issues first.
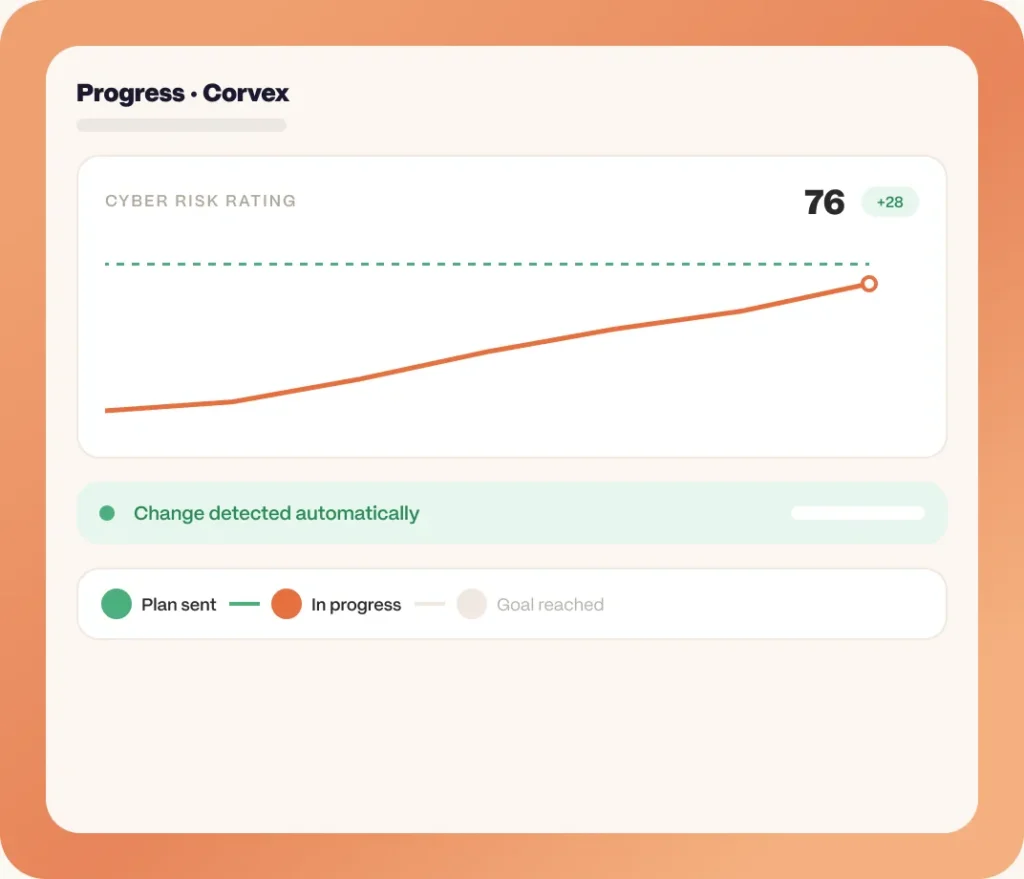
See Remediation Plan Progress Automatically
As your suppliers progress with their remediation plans, the changes are automatically detected and reflected on the Panorays platform.
The Unique Capabilities of Panorays’ Cyber Risk Ratings
Panorays provides clear and actionable information that allows us to easily prioritize how to remediate our suppliers’ cyber gaps.
 Itzik Menashe, VP IT & Information Security, Telit