
IndustriesTechnology
Third-Party Cyber Risk Management for Technology Companies
For Technology companies, staying ahead of third-party risks is no easy task. From managing complex supply chains to ensuring business continuity, CISOs prioritize third-party risk management to protect their businesses from breaches and supply chain attacks.
99.8 %
risk rating accuracy
+ 98 %
third-party questionnaire response rate
− 80 %
third-party onboarding time
Complete Control Over Third-Party Risks
Tackle Supply Chain Complexity
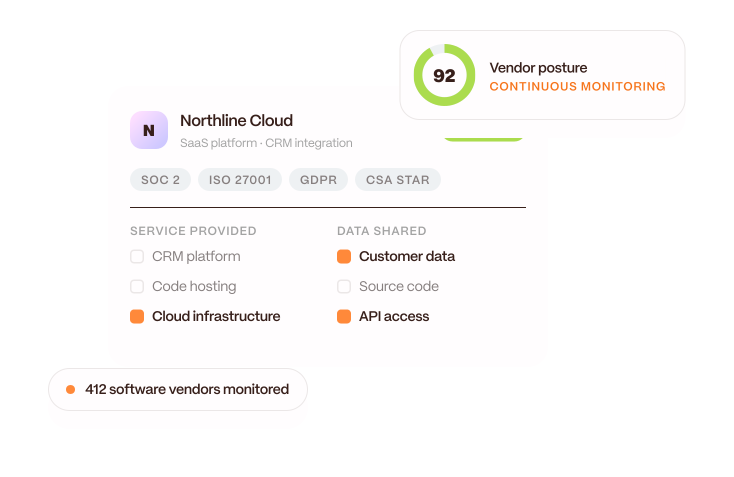
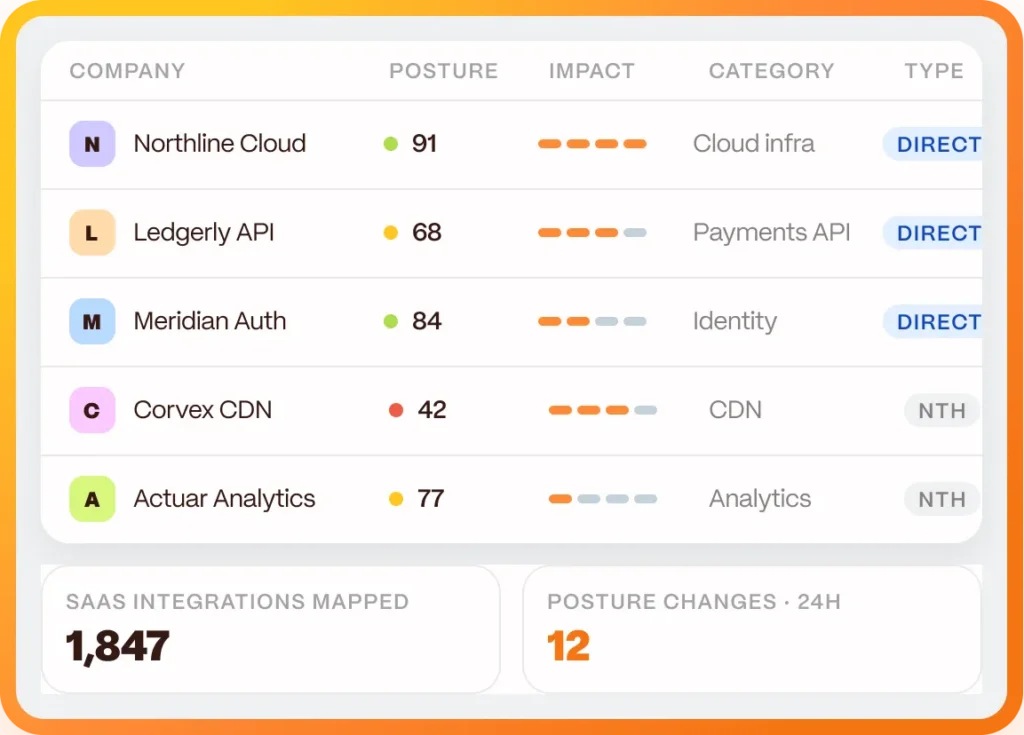
Manage your complex supply chain and easily assess the security postures of all software vendors and integrations. Gain visibility into your third parties’ security postures and manage each relationship with remediation steps and in-platform communication.
Confidently Manage Your Supply Chain Exposure With Panorays
Minimized Response Time to Attacks
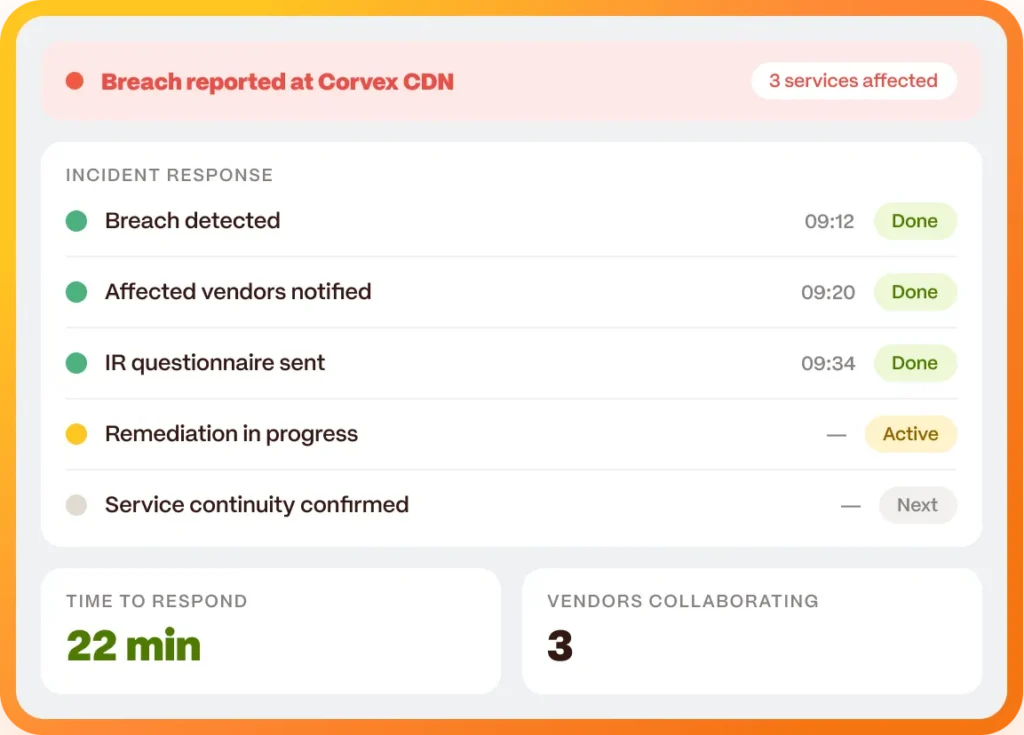
Get real-time insights into cyber attacks with automated security monitoring and alerts, mitigate the impact of breaches and maintain service continuity.
Complete Supply Chain Visibility
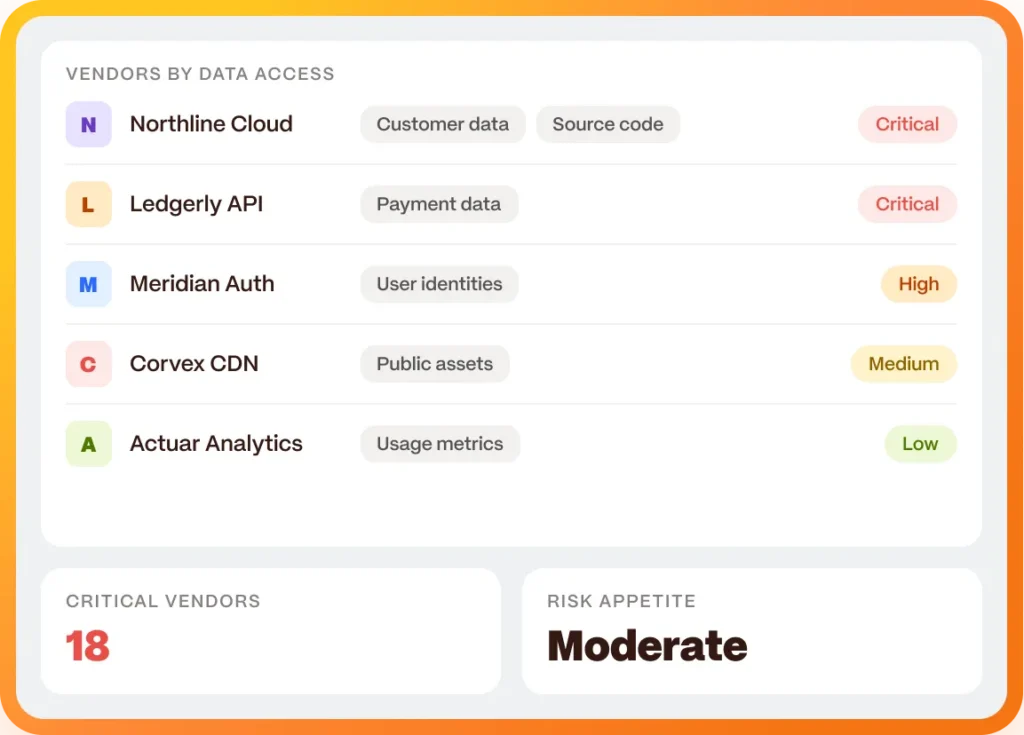
With comprehensive visibility into the security posture of your third parties, you can easily monitor the security practices of your vendors, prevent vulnerabilities and ensure that all security standards are met across the supply chain.
Respond to Vulnerabilities
Proactively respond to vulnerabilities by leveraging detailed insights into your third-parties’ security gaps. Remediate potential security gaps promptly and maintain a robust defense against potential cyber threats.
Tech Companies Rely on Panorays to Protect Their Supply Chains
Panorays provides us with an extensive amount of information about potential vendors, way beyond what we would be able to find on our own. This enables us to make quick and informed decisions about vendor selection.
 Esther Pinto, Information Security Team Leader, AppsFlyer
When you have a product like Panorays, you gain greater confidence about your vendor due diligence because you can dig deeper
 Ra’Monne Hayes, Director of Information Security, Sisense
With Panorays, we have a more comprehensive view of our suppliers. We have a better understanding of who we are dealing with, what are their levels of security and privacy, what permissions they need, and what data they use.
 Daniel Chechick, CISO, WalkMe
Stay Ahead of Third-Party Breaches With Panorays
Vulnerability Risk Management and Third Party Risk
Earlier this month American Express announced it suffered a third-party data breach. Although it is not known how many of its customers…
How To Prevent Data Breaches in 2024: 7 Best Practices
The average IT organization has an average of 25 third parties and a fourth or fifth-party relationship with over 200 parties. With…
3 Essential Third-Party Cyber Risk Insights for CISOs in 2024
Gain critical insights from the latest 2024 CISO Survey on third-party cyber risk in 2024.